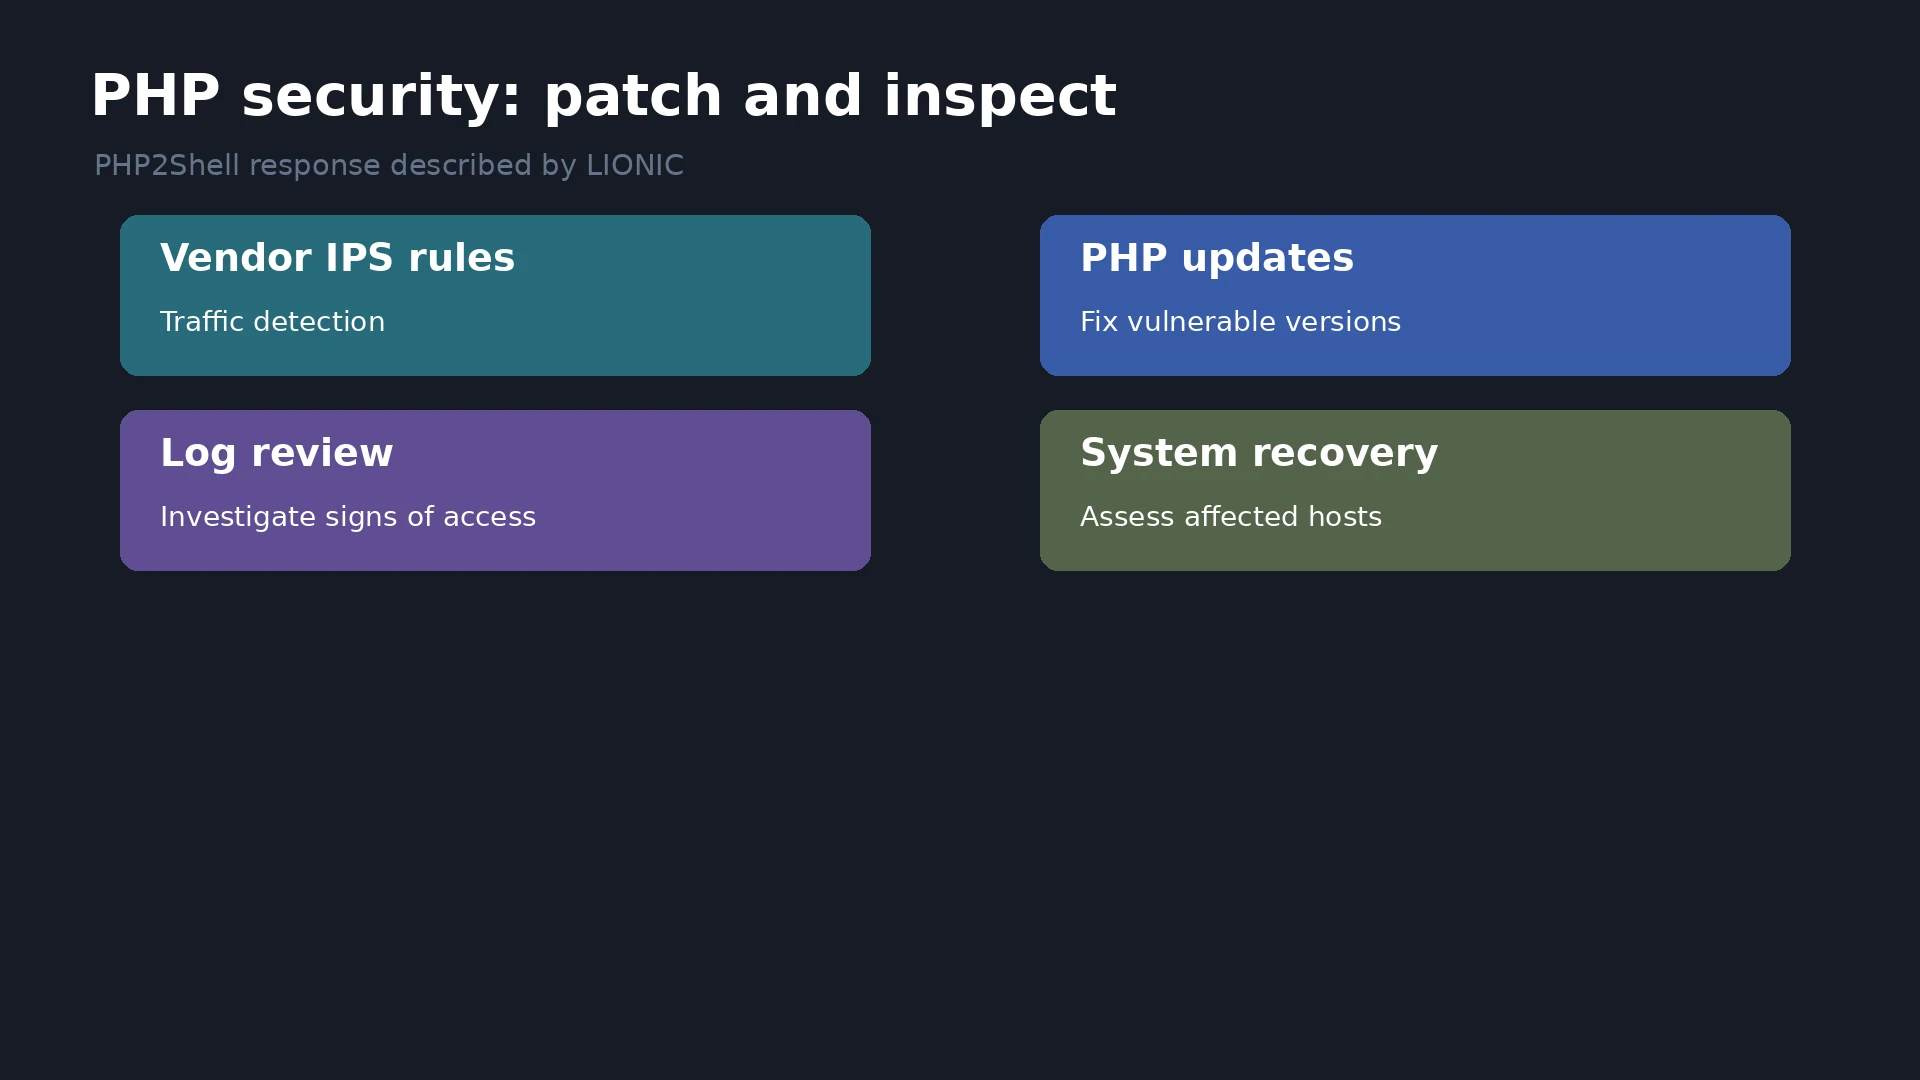
LIONIC announces IPS rules for PHP2Shell alongside the PHP security fixes
LIONIC has announced intrusion-prevention rules targeting PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. The company says its IPS protection can provide a temporary additional layer for organisations preparing to update their PHP environments.
The issues affect request handling and can lead to memory corruption and, under applicable conditions, unauthenticated remote code execution. The PHP security updates address out-of-memory error handling and stale request state. The UK NCSC has confirmed the advisory and urged organisations to identify affected installations.
The corrected upstream releases include PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. LIONIC lists protection signatures 8106730, 8106731 and 8106732 for the two vulnerabilities.
Coverage depends on the rules, product version and deployment. LIONIC states that network-level protection does not replace the official PHP security updates.
Инфографика: SE7EN.ws. Editorial diagram based on LIONIC and PHP advisories.
Related articles
 Balance on the Edge of Data: Alexander Grif on Why Privacy Has Become an Illusion and Data a New Weapon
 Darude Releases Sandstorm Storm 25 Mix After Reworking the Track for His Anniversary Tour
 Mahmut Orhan and Felix Raphael Release Three
 Gabry Ponte releases festival anthem Pulse React
 Prime 1 Studio opened preorders for an 86.8 kg Queen Alien statue
 Mosimann and Gaetan Roussel Release New Single Soon
 Michelle Yeoh receives a star on the Hollywood Walk of Fame
 Bitcoin’s Growing Role in Corporate Strategies and Market Sentiment